by laura warde | Apr 30, 2024 | 2024 News, Blogs, News
Auckland, New Zealand – 30 April 2024
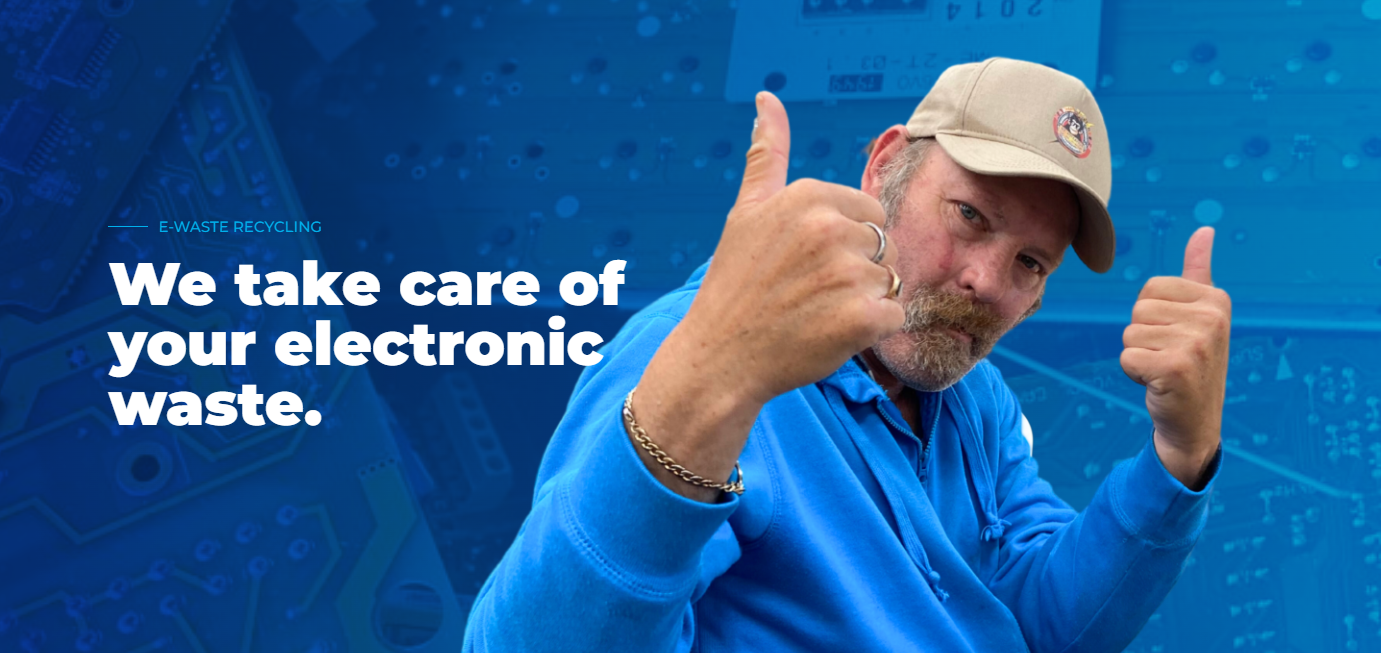
Lexel Systems, a leading IT company based on the North Shore, is proud to announce its community partnership with The Abilities Group, a distinguished non-profit organisation dedicated to empowering individuals with disabilities through meaningful employment and community integration.
With a rich history of service dating back to 1959, The Abilities Group has been a beacon of hope and empowerment, helping individuals with disabilities to achieve independence and contribute to the community. Their diverse programs range from employment and training to environmental initiatives, demonstrating a holistic approach to social and vocational development. Through this partnership, The Abilities Group collects all the IT hardware recycling from Lexel Systems and its customers in an initiative to protect the environment and reduce waste.
“We are proud to partner with The Abilities Group, an organisation whose values align with Lexel’s commitment to community and inclusivity,” said Troy McCallum, Procurement Services Manager at Lexel Systems. “This partnership reflects our dedication to not only advancing technology but also enriching the lives of those in the community around us.”
Through this initiative, Lexel Systems aims to bring more awareness to the crucial work done by The Abilities Group and to encourage other businesses and individuals in Auckland to join in supporting this noble cause. Lexel Systems believes in the power of community and the significant impact that collective support can have on local non-profit organisations.
“We invite our customers, partners, and the public to learn more about The Abilities Group and to explore ways they can contribute to making Auckland a more inclusive and supportive community,” added Alison Renwick, Marketing Manager at Lexel Systems.
For more information about The Abilities Group and the services they provide, please visit their website at www.abilities.co.nz.
by laura warde | Apr 23, 2024 | 2024 News, Blogs, News
In today’s digital landscape, data is not just an asset; it’s the critical backbone of business continuity. Knowing this, your data backup and recovery strategies need to be robust and foolproof. However, the truth is many businesses are navigating these defence strategies and crucial processes with only a partial understanding and even worse, a partial implementation of their chosen solution. Often, small and medium-sized businesses are trying to manage this element of risk themselves, but they just don’t know what they don’t know…
Here are some tips to ensuring that your business is not just running – but operating according to best practices, with optimal data security and management to reduce your risk.
1. Diagnose the Unknown
In some cases, business leaders are not aware of the pitfalls in their IT environments until something fails. This reactive approach can lead to significant downtime, financial losses, brand damage and unexpected outcomes. Shift your strategy from reactive to proactive. A deep dive into your IT environment can pinpoint why failures occur and identify what is causing inefficiencies or security vulnerabilities in your current setup.
Not all setups are created equal, and what works for one might not be the best for another. Many businesses implement solutions based on generic advice and best-guess scenarios etc, which may not fully align with specific needs or compliance requirements. By evaluating whether your systems are optimally configured, you will better understand what is missing and can investigate adjustments to enhance performance and security.
3. Follow Best Practices
In the age of increasing cyber threats, feeling confident about your data security is non-negotiable. By ensuring that your backup and recovery setups are the best they can be for your business, make sure you follow best practices suited to your specific business needs. This reassurance is vital, especially in protecting against and recovering successfully from malicious attacks.
4. Go All In
It’s a common scenario: with the best of intentions, IT Managers or Systems Managers half-read the manual and half-implement a solution. Without a high level of skilled and experienced staff to set up and maintain intricate data backup and recovery systems, this approach often leads to unexpected failures. Make sure your chosen solution is the best fit for your business and make sure that you’re fully implementing and managing the system to offer the best protection.
Instead of leaving the responsibility of your data backup and recovery solution to rest on the shoulders of one person within your business, partnering with a trusted provider will give you a greater advantage. This is where Lexel Systems can step in to take a comprehensive look into your environment. We assess your current implementation, identify any areas of risk, and provide expert advice on how to enhance your system’s reliability and security.
Don’t let the unknown be your downfall. Empower your team to focus on what they do best driving your business forward, while we handle the intricacies of your data protection needs. Let’s move beyond the halfway mark together, ensuring a fully secure, optimally configured, and expertly managed IT environment. We don’t just fill in the gaps; we expand your capabilities, enabling your business to grow securely and efficiently.
Take the first step towards complete data assurance; contact Lexel today.
Get in touch
Author:
Etienne van der Berg
Etienne is an experienced professional with over 20 years of working in the IT Industry. As a Principal Consultant at Lexel, his area of expertise is around Backup and Recovery where he works with our customers to help with backups of virtual, physical, and cloud-based workloads, and capturing all their data in a consistent state that can be used for faster recovery in the case of an incident occurring.
by laura warde | Apr 11, 2024 | 2024 News, Blogs, News
The data centre is no longer the centre of a business.
Traditionally, applications were hosted in the data centre and users regardless of where they were had to connect back to the data centre to access their business applications. With organisations transitioning to the cloud and software as a service (SaaS) applications, the way we work has changed.
In today’s evolving digital landscape, securing networks has become a complex challenge. Secure Access Service Edge (SASE) presents a unified approach to addressing these challenges, offering a security framework that caters to the demands of modern organisations.
SASE joins the functionalities of security and network connectivity into a single, cloud-native service. This integration provides an agile, scalable, and secure framework, capable of supporting the changing nature of business operations, including remote work, cloud computing, and mobile access.
For business leaders, understanding SASE is crucial. It’s a strategic shift that merges services, embraces the cloud, and prioritises zero trust.
Why SASE Matters
The significance of SASE lies in its holistic approach to network and security functions. Traditional security measures work in silos, creating complexities and gaps in defence mechanisms. SASE, on the other hand, offers a unified solution that simplifies management and enhances security across all network edges. Its cloud-native design allows businesses to adapt to changes swiftly, ensuring that security policies are consistently applied, regardless of the users’ location or the resources they access.
Benefits of SASE for Businesses
- Enhanced Security: SASE’s framework, which includes components like Zero Trust Network Access (ZTNA), Secure Web Gateways (SWG), and Cloud Access Security Brokers (CASB), provides robust protection against a wide array of cyber threats. By adopting a zero-trust model, you can ensure that access is strictly authenticated and authorised, significantly reducing the attack surface.
- Operational Agility: With SASE, businesses can rapidly adjust to new operational needs, such as setting up remote workstations or integrating cloud services. Its cloud-based nature allows for quick deployment and scaling, catering to the needs of businesses.
- Cost Efficiency: By combining multiple security services into a single platform, SASE helps reduce the complexity and overhead costs associated with managing disparate security tools. This consolidation leads to a more cost-effective and streamlined security posture.
- Improved User Experience: SASE optimises network performance through intelligent routing and bandwidth management, ensuring high-quality connectivity for cloud applications and services. This results in a smoother, more reliable user experience for end-users, enhancing productivity.
Implementing SASE with Lexel and HPE Aruba
As you embark on this journey, consider partnering with experts who can guide you through this transformation.
Lexel, in partnership with HPE Aruba, delivers cutting-edge SASE solutions. Leveraging HPE Aruba’s robust SD-WAN and SSE technologies, Lexel provides a comprehensive service that not only secures your network but also enhances its efficiency and agility. With an emphasis on customer-centric solutions, Lexel tailors its SASE offerings to meet the unique needs of each business, ensuring a seamless and secure digital transformation journey.
As businesses navigate the complexities of modern IT environments, the need for a unified, efficient, and secure network infrastructure has never been more critical. SASE is a pivotal solution, addressing the challenges of network security and connectivity. With the expertise of our subject matter experts and technological backing of HPE Aruba, organisations can embark on a path toward a more secure, agile, and cost-effective network ecosystem, ready to thrive and adapt in the digital age.
Embracing SASE is not just about enhancing network security; it is about positioning your business for success in a world where agility, resilience, and security are paramount. If you are an IT and infrastructure manager, CEO, or business leader looking to future-proof your business, understanding, and implementing SASE with the experience and expertise of Lexel and Aruba is a strategic step toward owning your digital transformation.
For a more detailed exploration of how SASE can revolutionise your business, get in touch with our team and discover how to secure your decentralised IT environment effectively.
Get in touch
Author:
Jason Chai
Jason is a seasoned IT professional with over 25 years of industry experience with a specialised focus on guiding customers on their path to securing a modern workplace with zero trust.
by laura warde | Apr 5, 2024 | 2024 News, Blogs
With years of experience in finding the right people for the job, working both in internal recruitment and for recruitment agencies, I’ve learned a lot about what it takes to hire well. Hiring is a big deal – it’s not just about filling a spot on your team; it’s about finding someone who truly fits well and will help your business grow. I’ve seen how tough it can be for businesses, big and small, to find that right fit in a competitive market. And I know too well the high cost of getting it wrong.
It’s not just the obvious cost of hiring a bad hire (salary, benefits and the cost of recruitment). In an article from Human Resources Director (HRD) NZ, the cost is outlined as follows:
- Time wasted in hiring new employee
- Team morale + productivity decrease
- Time taken to onboard, train and gain value out of new employee
- Time taken to manage the employee out of the business
Time wasted in hiring a new employee
The time it takes to hire a new employee is unfortunately only getting longer. We are currently seeing record numbers of applications to job adverts; which sounds great – but is it really?
More applicants results in more time spent by internal talent teams or HR sifting through literally hundreds of applications for roles. It therefore takes longer to identify a preferred short-list of candidates, surfacing the risk of losing those preferred candidates, as they secure other opportunities through faster, more agile recruiters.
If the responsibility of screening applicants falls to the hiring managers, the screening process can take even longer. Taking them away from their day job to assess job applicants leads to a drop in productivity, increased stress, and even longer to get to shortlist stage.
End result: active candidates move further through competitors’ recruitment processes and may have already secured an alternative role by the time they are shortlisted. This could result in no hire being made due to a lack of quality candidates shortlisted and interviewed. The process starts again, resulting in more time that the vacancy remains unfilled, increased frustration and decreased productivity.
By relying solely on active job seekers applying to adverts, businesses are also missing out on accessing untapped passive talent pools of potential candidates – who, if targeted correctly, may be better suited than any ad response.
Team morale and productivity decrease
The longer a vacancy remains unfilled, the more work allocated to other team members – which is not only bad for morale but could lead to burn out or frustrations resulting in more turnover within the team.
End result: Missed deadlines and lost revenue due to decreased employee morale and increased staff turnover rates.
Time taken to onboard, train and gain value out of new employee
According to many online sources it takes roughly 90 days to start seeing the value of a new employee, which is broken down below:
1st month settling in and learning their new business,
2nd month performing tasks and learning from mistakes,
3rd month giving value back to the team and business
Each stage of this first 90 day period requires extensive time and input from other team members and management. If an employer invests in a new employee through the process above, only to find that they are either not performing or not the right fit for the team – productivity and morale across the team will drop further and costs increase.
End Result: Loss of time and money spent on the onboarding process, team morale and productivity decrease further.
Managing the employee out of the business
The longer this process takes, the more negative impact this will have on the team and the business as a whole.
End result: If a team manager tolerates a team member who is not performing – the more likely the high performing team members are to look for a new opportunity themselves and the reputation of the leader is severely compromised.
The consequences of a bad hire go much deeper than just financial setbacks. It’s a situation that affects everything from productivity and team morale to turnover, not to mention the broader implications for your employment brand and reputation. This supports the vital need for a strategic approach to recruitment. In our search for talent, compromising quality for speed is a pothole we must avoid.
In the evolving landscape of talent acquisition, limiting your search to just active job seekers could mean missing out on top-tier candidates. Many highly qualified professionals aren’t actively scanning job listings, but the right offer, presented in the right way, can generate their interest. That’s where the value of partnering with a reputable recruiter comes into play. A good recruiter has the skills to delve into passive talent pools, reaching out to and engaging the best talent available. This approach not only enhances the quality of your candidate shortlist but also ensures your brand and value proposition is communicated professionally and consistently.
At Lexel Resourcing, we provide bespoke solutions tailored to meet the unique needs of each client, aimed at attracting and securing the best talent out there. Our approach encompasses innovative sourcing tools, sophisticated assessment methods, and strategic onboarding practices, all designed to refine and optimise the hiring process. Reach out to our team, and let’s discuss how we can help strengthen and solidify your workforce for the future.
Get in touch

Author:
Andy Talbutt
With more than 20 years in the talent and people business; Andy has held a mixture for recruitment and HR roles; locally and internationally, mainly within IT and corporate organisations.
by laura warde | Apr 3, 2024 | 2024 News, Blogs, News
We recently hosted an industry lunch to discuss shared challenges businesses are facing with the increase in cyberattacks. Following the event, I thought it worth sharing a few points you should be considering based on the conversations we have had, to help you consider your approach and hopefully help speed up the adoption of change.
I think it is fair to say that most organizations acknowledge the threat cybercrime presents and have already invested significantly (in money and in effort) to reduce the risk of cyberattacks in recent years. Despite businesses choosing from over 3,000 security providers and spending nearly $170 billion globally per year (2022), cyberattacks are still causing huge losses, growing from $3 trillion in 2015 to an expected $10.5 trillion by 2025. This highlights the need for businesses to find better ways to use security tools and build on their capabilities. Businesses need to move to more effective security operations and disrupt the trajectory of cyberattacks.
In one discussion around cyber response, a customer’s made a poignant comment: “After a cyber incident, we won’t be measured on our response but rather on what wasn’t protected”.
I think this is a good summary of the dilemma most businesses face and a good starting point on how to expand the conversation. Two areas Lexel is focused on are:
– Security Challenges
– How to improve effectiveness
Let us break down what each involves:
Security Challenges
From industry best practices and my experience on this topic, I would say the security challenges can be broken down into five primary areas:
1. Malicious activity
Self-explanatory really, all attacks have nefarious intent.
- Cybercriminals are paid to breach your security setup and steal data they can hold for ransom – it’s their job.
2. Compliance drivers
- Often driven by changing regulations.
- Business partners may prescribe minimum security requirements (see Embrace Security Operations below).
- If a breach takes place, fixing the issue is no longer enough, Auditing the Failure is key.
- Assessment of Gaps is a constant requirement. There needs to be: A unit of measure A process to expedite change requirements at a board level Understanding by businesses what the risks truly are (there is nowhere to hide anymore).
- Legal and compliance requirements are increasing and will continue to do so. The time to get your house in order is now.
3. Security dissatisfaction with current tools/approach
Most businesses are operating with good intent. Even when significant investment has been made in tools to protect that business, for many, the cyber threat still exists. This is because of:
- Security dysfunction from the cost of the tools i.e. spending money on multiple tools but not realising the true potential of each.
- It has become too complex to manage.
- Too much noise – simply too many false positives from the tools which makes it exceedingly difficult for businesses to react to genuine threats.
4. Resource Constraints
There is a talent shortage in this space and in reality, one resource is not enough. To effectively protect a business, “eyes on glass” 24/7 is a requirement, not just a “nice to have”. To properly resource a SOC 24/7, you would typically need between 8-12 Security Analysts (depending on size) to account for sick leave, annual leave, shift times. Additionally, “eyes on glass” effectiveness for any resource is generally no more than 4hrs in a single session.
5. Cyber Insurance Gaps
There is often uncertainty as to what is covered by insurance and under what circumstances claims will be paid. Many businesses either have insurance but are not confident claims will be paid or have found it too difficult to get suitable cyber security insurance based on the terms specified by insurance companies. In summary businesses operate under:
- Reduced coverage
- Increased rates
- Ransomwares carve outs (those exclusions of cover introduced by insurance companies)
How to improve effectiveness
Once there is a sound understanding of the Security Challenges above, there is a well-established process that can be followed to improve your current position. This can be broken down as follows:
Optimise:
- Make sure all current security investments are being fully utilised
Leverage your existing data:
There is often significant information available from existing tools set up in a business that you can leverage. By fully understanding what information you already have about your network, you can make more informed decisions about what you need. Ask yourself the following questions:
- Am I generating real value from the information already?
- How am I measuring this success?
- How is success being measured?
- How does the business Embrace Security Operations?
Find a standard that meets your commercial requirements:
If your business has not found a standard to compare against, this should be high on your priority list. There are well-established frameworks like Essential Eight and NIST (National Institute for Standards and Technology) you can investigate. These frameworks will help your business to succeed. Terms to focus on are:
- Identify
- Protect
- Detect
- Respond
- Recover
- In addition to the above, cover all attack surfaces, identified as: Endpoint Network Cloud Identity Human
- Build Resilience
Build an effective Cyber Threat Response:
What is important to note is this is not a single project you set and forget. The art of building a resilient Cyber Threat Response includes:
- Sustain improvements, this is not a single event, rather a lifestyle change
- Add Expertise, this is one of the biggest challenges for any business
- Implement 24×7 protection “eye’s on glass” – arguably the hardest part of the response plan
- Getting ahead of the threat requires applying tactical and strategic actions. This is part of your Cyber Threat Response plan
- There needs to be a mindset that this is a journey not an event. You should strive to constantly elevate and adjust their security posture
In Summary
Managing your cyber threat environment is not about finding one vendor that does everything. Having the ability swap out aspects from time to time is important. Having a Cyber Threat Response is more a process and a construct rather than a specific product.
A Cyber Threat Response should include:
- Prevention
- Detection
- Creating and following a Cyber Respond Plan
- Evaluating and updating to remain compliant and build resilience
If you’d like to discuss further or find out more about how you can set up your own Cyber Threat Response, get in touch with us here.